Can You Prove What Happened in Your Integrations?
When an auditor asks what happened to a specific transaction, can your team provide a clear answer?
Most IT teams have logs to monitor systems and investigate errors. But knowing that a system was running is not the same as proving what happened to a particular message, when it happened, and which controls were in place.
That distinction matters during audits and compliance reviews.
Without reliable, searchable records, teams may spend days gathering logs from different systems, matching timestamps and reconstructing events. Even then, the evidence may be incomplete.
The real value of traceability is being able to find reliable answers without rebuilding the history.
How Nodinite supports traceability
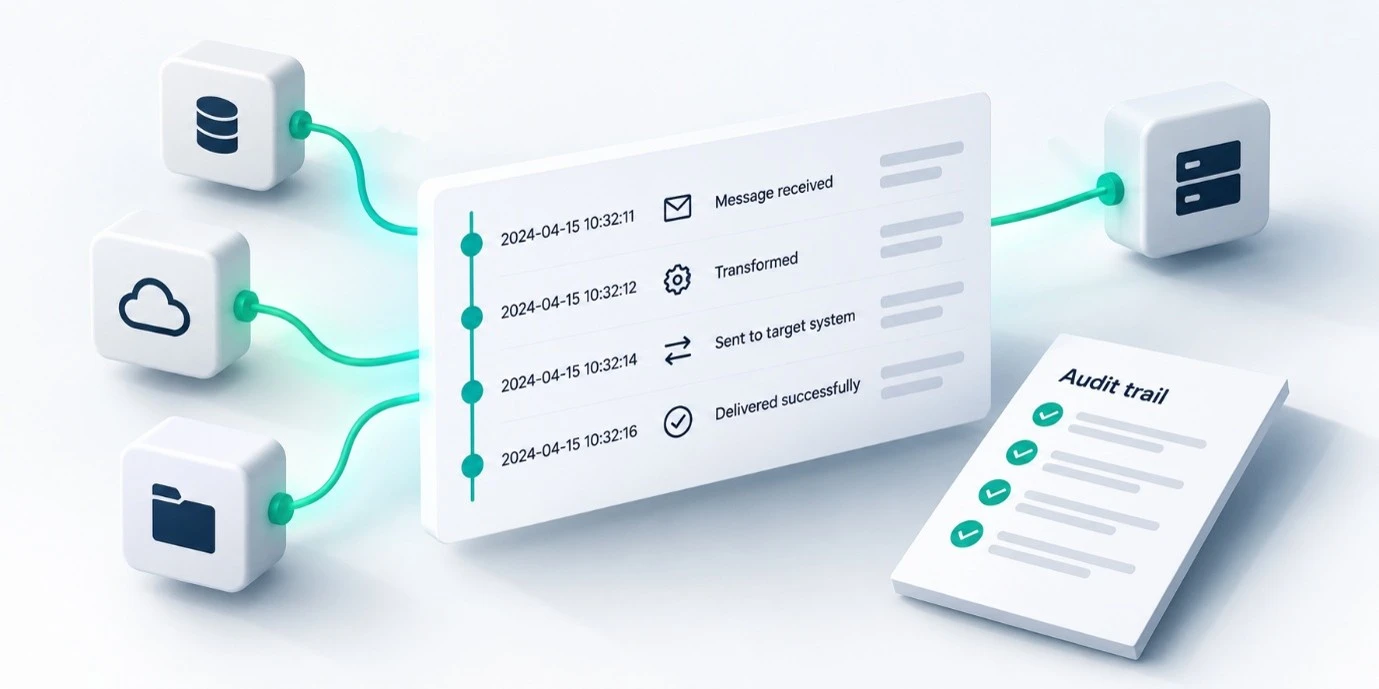
Nodinite helps organisations track transactions across integrated systems. With properly configured logging and search fields, teams can find individual messages, review recorded events and timestamps, and follow transactions across systems.
Role-based access and audit logging also help organisations control who can view sensitive information and track access to it.
However, traceability depends on what information is logged and how long it is retained. Good configuration and appropriate retention policies remain essential.
A simple test for your IT team
Choose one business-critical integration and ask:
Can we find exactly what happened to a specific transaction six months ago?
If answering requires several people and hours of investigation, there may be an opportunity to improve your traceability.
Because when the next audit arrives, having the evidence readily available makes all the difference.
Further reading: What is a Log View?